
01
Cybersecurity testingProtect your business
Find security weaknesses and understand what to fix first.
View services
Cybersecurity testing, compliance readiness and software testing. Clear priorities to protect your information and keep your business moving.
About 8–10 minutes · No technical knowledge needed
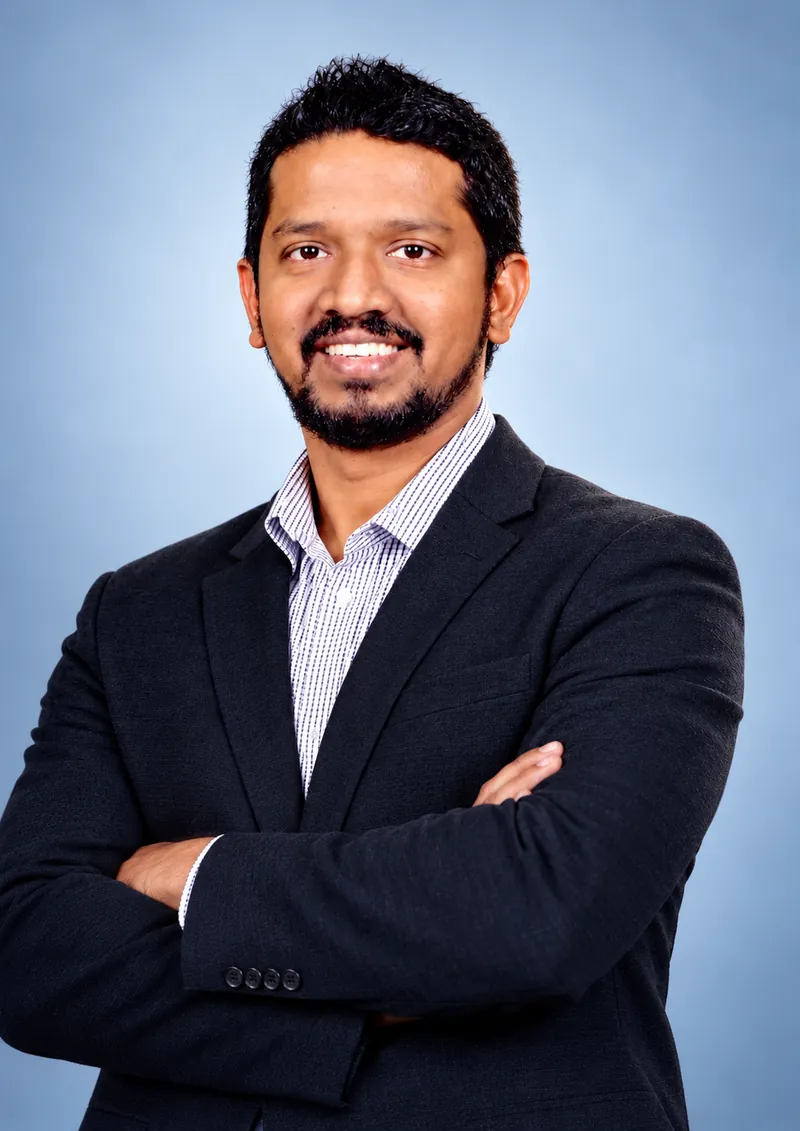
Sam Embuldeniya helps businesses turn technology concerns into practical priorities. We start with how your business works, explain the options and agree a scope that suits your needs.
Based in Gippsland, helping businesses across Australia.
About Sam and CYRENTIQChoose the outcome that matters to your business.
Find security weaknesses and understand what to fix first.
View servicesUnderstand what customers and standards ask for, then plan the next steps.
View servicesCheck that your apps work as expected before customers use them.
View servicesSeven credentials held across our team. Explore the testing capabilities behind them.
Offensive Security Experienced Penetration Tester
Explore how weaknesses could combine into a more serious attack.
Offensive Security Certified Professional
Identify and validate weaknesses in systems within an authorised scope.
Certified Red Team Operator
Examine how realistic attack scenarios could challenge your defences.
Certified Red Team Expert
Investigate how connected systems and access could increase business risk.
Certified Red Team Professional
Explore weaknesses in account permissions and internal access.
eLearnSecurity Certified Professional Penetration Tester
Turn technical testing findings into clear risks and practical priorities.
eLearnSecurity Junior Penetration Tester
Apply a structured approach to discovering and assessing weaknesses.
Individual team-member credentials, not company certifications. Practitioners are matched to your scope; not every team member holds every credential.
Scope, permission and fees confirmed before work begins.
Evidence and priorities explained in plain English.
A practical handover matched to your team and resources.
Tell us what you want to improve. We’ll help you define the scope.